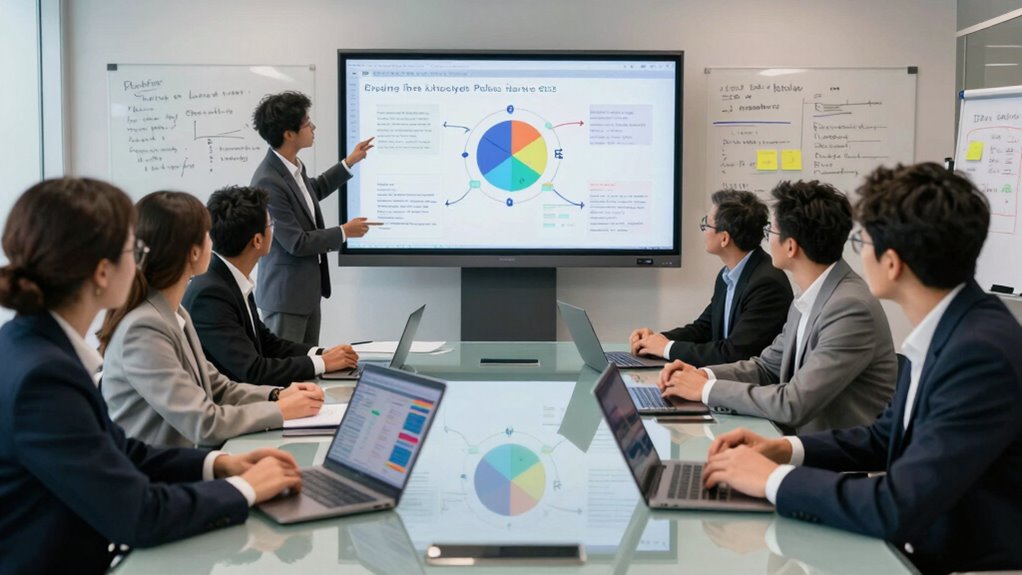
To build a data lifecycle policy your team can follow, start by defining clear governance rules and assigning roles like data owners and stewards. Map out each stage from data creation to disposal and implement security controls such as encryption and access restrictions. Guarantee compliance with regulations like GDPR or HIPAA, and document every step for accountability. Regularly review and update the policy to adapt to new regulations or technologies, and discover more ways to strengthen your approach as you continue exploring this guide.

Get business pricing on networking and server gear
- Business-only prices and quantity discounts
- Tax-exempt purchasing
- Multiple users, one account, clear invoices
Key Takeaways
- Define clear roles and responsibilities, including data stewards and owners, for accountability at each lifecycle stage.
- Map the entire data lifecycle, from creation to disposal, to establish appropriate management and security controls.
- Develop standardized procedures for data collection, storage, usage, retention, and deletion aligned with compliance standards.
- Document all data handling processes thoroughly to ensure transparency, audit readiness, and regulatory compliance.
- Regularly review and update the policy to adapt to technological, regulatory, and organizational changes.
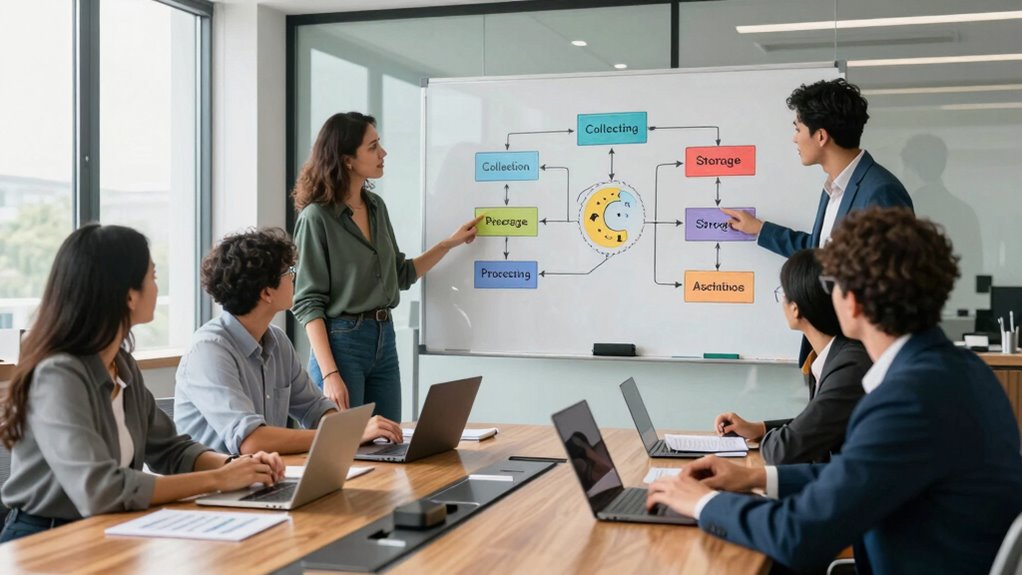
Creating a data lifecycle policy is essential for managing your organization’s data effectively, guaranteeing it remains secure, compliant, and accessible throughout its lifespan. To do this successfully, you need a clear understanding of data governance, which involves establishing rules and responsibilities for data management. Data governance helps you define who can access data, how it’s used, and how it’s protected, creating a foundation for a strong data lifecycle policy. Compliance standards play a critical role here, as regulations like GDPR, HIPAA, or CCPA set specific requirements for data handling and security. Your policy must align with these standards to avoid legal risks and penalties.
Start by mapping out the entire data lifecycle, from creation and collection to storage, usage, sharing, archiving, and eventual disposal. Knowing each phase allows you to identify what security measures, controls, and documentation are necessary at every stage. For example, during data collection, you should guarantee that data is obtained ethically and with user consent, aligning with applicable compliance standards. When storing data, implement encryption and access controls based on your governance policies, so only authorized personnel can access sensitive information. Understanding the importance of data classification helps in applying appropriate security measures to different types of data. Additionally, recognizing the data lifecycle stages ensures comprehensive management across all phases. Incorporating data management practices that are aligned with industry standards further strengthens your approach. Regularly reviewing these practices ensures they stay current with evolving technologies and regulations.
Next, define clear roles and responsibilities within your team. Assign data stewards or data owners who oversee specific datasets, ensuring accountability for compliance and security. These individuals should be well-versed in your governance framework and compliance obligations. Establish procedures for regularly reviewing and updating data, especially when it’s no longer needed or when regulations change. This proactive approach helps prevent data sprawl and minimizes risks associated with outdated or non-compliant data.
Your policy should also specify retention periods for different data types, grounded in legal and operational needs. Automate the deletion of data once those periods expire, guaranteeing compliance with data minimization principles. Make sure your team understands the importance of documentation at every step, from data collection to disposal, so you can demonstrate compliance during audits. Regular training sessions reinforce these practices, keeping everyone aligned with governance policies and standards. By maintaining clear documentation, organizations can also streamline audit readiness and support transparency.
Finally, embed monitoring and auditing processes into your policy. Continuous oversight helps detect breaches or violations early, allowing you to respond swiftly. Using tools that track data access and modifications supports transparency and accountability. Incorporating effective data management practices into your policy ensures that your data remains secure, compliant, and well-governed throughout its lifecycle. Your data lifecycle policy isn’t static; it should evolve with changing regulations, technology, and organizational needs. By emphasizing data governance and compliance standards throughout the lifecycle, you ensure your data remains secure, legally compliant, and used effectively to support your organization’s objectives.
As an affiliate, we earn on qualifying purchases.
Frequently Asked Questions
How Often Should Data Lifecycle Policies Be Reviewed and Updated?
You should review and update your data lifecycle policies at least annually, ensuring they align with current data retention requirements and compliance standards. Regular policy audits help identify outdated practices or gaps, so schedule these reviews consistently. By doing so, you maintain data security, comply with regulations, and optimize data management processes, reducing risks associated with data retention and ensuring your policies stay relevant in a changing data landscape.
What Tools Are Recommended for Managing Data Lifecycle Processes?
You should use tools that help manage data retention and access controls effectively. Recommended options include data governance platforms like Collibra or Informatica, which automate data lifecycle processes, enforce policies, and monitor access controls. These tools enable you to set retention periods, restrict data access, and guarantee compliance. They simplify managing data throughout its lifecycle, reduce risks, and improve overall data security and compliance.
How Do We Ensure Compliance With Data Privacy Regulations?
Imagine your team faces a regulatory audit, and you need to demonstrate compliance. To guarantee this, implement data anonymization techniques to protect sensitive information and meet privacy standards. Regularly review your data lifecycle policies, stay updated on regulations, and document your compliance efforts. This proactive approach helps you avoid penalties, builds trust, and ensures ongoing adherence to data privacy regulations during audits.
Who Should Be Responsible for Enforcing Data Lifecycle Policies?
You should assign data stewardship responsibilities to a dedicated team or individual to guarantee policy enforcement. As a data steward, you’re responsible for overseeing adherence to data lifecycle policies, including data creation, storage, and deletion. By clearly defining roles and empowering stewards to monitor compliance, your team can effectively enforce policies, maintain data integrity, and ensure regulatory adherence. Consistent policy enforcement relies on proactive oversight and accountability.
How Can Teams Handle Data Breaches or Accidental Data Loss?
Imagine your data as a fortress; when a breach occurs, you act swiftly like a vigilant guard. You should have an incident response plan in place, ready to contain and assess the breach or data loss. Regular breach prevention training and audits strengthen defenses. Quickly isolating affected data, notifying stakeholders, and reviewing security measures help minimize damage, ensuring your team can respond effectively and protect critical information proactively.
access control software for data security
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Conclusion
By crafting a clear data lifecycle policy, you’re planting a sturdy tree that bears consistent fruit—trustworthy, well-managed data. Remember, it’s not just about setting rules but nurturing a culture where data flows smoothly from creation to deletion. Keep your policies simple and adaptable, like a river that finds its way around obstacles. With this approach, your team will sail confidently through data management, turning information into your greatest asset rather than a sinking ship.
As an affiliate, we earn on qualifying purchases.
data governance compliance software
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Halloween Picks
halloween
As an affiliate, we earn on qualifying purchases.