A thorough safe storage policy helps prevent ad hoc security habits by establishing clear, consistent procedures for securing valuables. You should combine physical locks with digital encryption, limit access to authorized personnel, and assign structured roles and permissions. Regularly monitor access logs and update permissions to catch vulnerabilities early. Promoting ongoing training and fostering a culture of security awareness ensures everyone follows the same standards. Keep exploring to learn how to build an effective system that works seamlessly.
Play games included with Prime
Start a Prime free trial and play with Amazon Luna on your devices.
As an affiliate, we earn on qualifying purchases.
Key Takeaways
- Implement centralized management of access rights to ensure consistency and accountability.
- Establish standardized procedures for access control, encryption, and security practices.
- Regularly review and update permissions to prevent unauthorized access.
- Use automated logs and monitoring to detect vulnerabilities and enforce security protocols.
- Promote ongoing staff training to reinforce disciplined security habits and awareness.
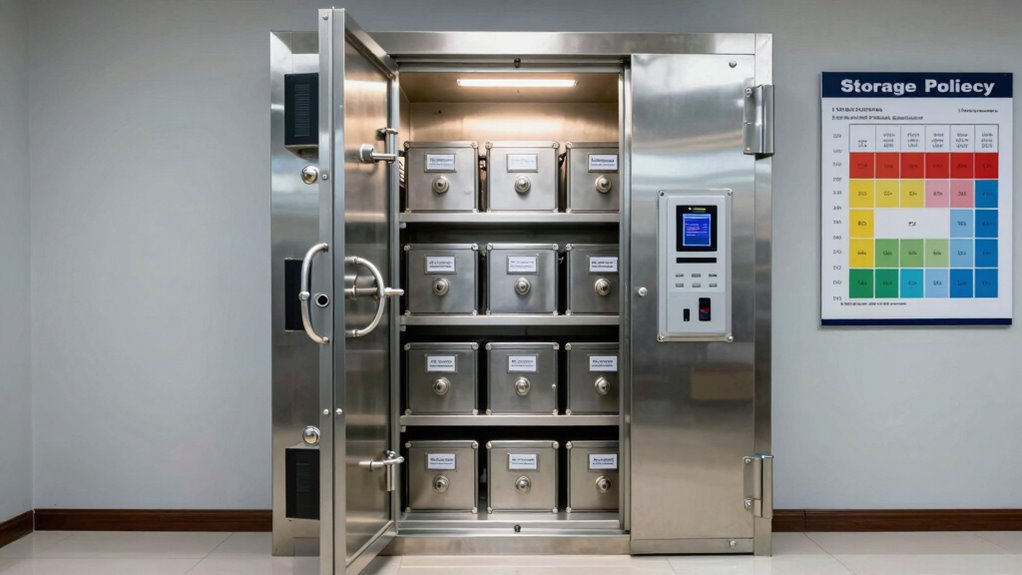
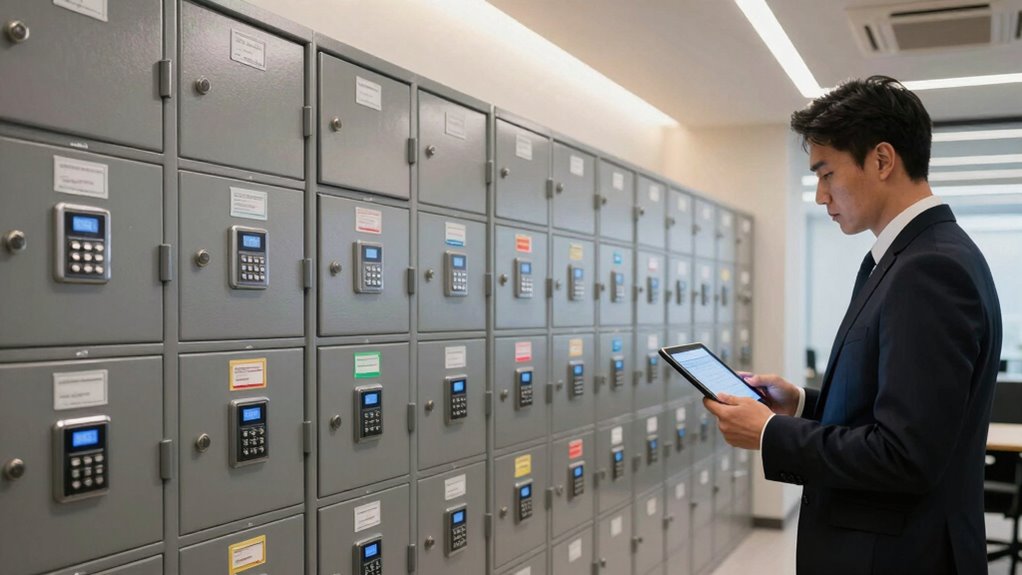
Have you ever wondered how to guarantee your valuables are protected and easily accessible? Implementing a solid safe storage policy is essential, especially when it comes to preventing ad hoc security habits that can leave you vulnerable. Relying on quick fixes or inconsistent practices often creates gaps in your security system, making it easier for unauthorized individuals to access sensitive information or valuables. The key lies in establishing clear, consistent procedures that everyone understands and follows. This means setting up structured access control measures, so only authorized personnel can reach certain areas or data. Access control isn’t just about physical locks; it also involves digital encryption to safeguard electronic information. Digital encryption transforms your data into unreadable code unless someone has the right decryption key, adding a vital layer of security for digital assets. When you combine access control with digital encryption, you create a robust barrier that prevents unauthorized access both physically and digitally.
A well-designed safe storage policy emphasizes the importance of centralized control over who can access what. Instead of relying on ad hoc practices—like handing out keys randomly or sharing passwords casually—you establish specific roles and permissions. This approach guarantees accountability and minimizes the risk of accidental exposure or theft. For example, you might designate certain employees as only able to access physical safes during specific hours, while digital access is granted through secure, encrypted channels. Regularly reviewing and updating these permissions keeps your security tight, especially as personnel or operational needs change. Incorporating a comprehensive security framework ensures that all aspects of your storage policies work together effectively. Additionally, implementing automated access logs can help you track usage patterns and identify potential vulnerabilities before they become issues. Creating a culture of ongoing security training educates staff about best practices and helps reinforce disciplined security habits. Establishing a formal policy also helps prevent the formation of inconsistent, ad hoc practices that can undermine your security efforts. Moreover, adopting standardized procedures ensures consistency across all security measures, reducing the likelihood of oversight. Ultimately, the goal is to prevent the formation of random, ineffective security habits that leave you exposed. Instead, you want a disciplined system where access is granted thoughtfully, data is encrypted properly, and security is an ongoing priority. By doing so, you not only safeguard your valuables but also create a culture of security awareness that minimizes risks and builds trust.
digital safe with biometric lock
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Frequently Asked Questions
How Often Should Storage Policies Be Reviewed and Updated?
You should review and update your storage policies at least once a year. Regular storage audits help identify vulnerabilities, ensuring your policy remains effective. A policy refresh keeps your security measures aligned with evolving threats and organizational changes. By maintaining a consistent review schedule, you minimize the risk of ad hoc security habits forming, ensuring your storage practices stay secure and compliant over time.
What Specific Training Is Provided for Staff on Safe Storage Practices?
You receive specific training focused on staff awareness of storage protocols, emphasizing the importance of secure handling and proper storage practices. This training includes hands-on demonstrations, clear guidelines, and regular refreshers to reinforce safety habits. You learn how to identify potential risks, implement best practices, and understand the consequences of lax storage. This proactive approach guarantees everyone understands their role in maintaining a secure environment and preventing security breaches.
How Does the Policy Address Storage of Sensitive Digital Data?
You guarantee sensitive digital data is protected by following encryption protocols, making it unreadable without proper keys. The policy mandates strict access controls, so only authorized personnel can view or modify this data. Regular audits verify compliance, and secure storage solutions prevent unauthorized access. By actively applying these measures, you prevent data breaches and maintain data integrity, aligning with best security practices and organizational standards.
Are There Penalties for Non-Compliance With the Storage Policy?
Yes, there are penalties for non-compliance with the storage policy. You’ll face compliance enforcement actions, which may include formal warnings, mandatory retraining, or other penalty measures. Repeated violations can result in more severe consequences, such as suspension or termination of access to sensitive data. It’s vital to follow the policy diligently to avoid these penalties and help maintain the security standards necessary for protecting digital information.
What Tools or Technologies Support the Implementation of the Policy?
Think of your security tools as the superhero duo—Encryption protocols and access controls—fighting off the villains of data breaches and unauthorized access. You support your policy by deploying encryption to scramble sensitive info and access controls to guarantee only the right heroes get in. These technologies work together, like a well-oiled security team, making sure your storage habits stay safe, consistent, and far from ad hoc chaos.
secure access control system for valuables
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Conclusion
Implementing a safe storage policy is essential to prevent ad hoc security habits that leave your information vulnerable. By establishing clear guidelines, you minimize risks and guarantee consistent security practices. Did you know that 60% of data breaches are caused by human error or negligence? Staying vigilant and disciplined with your storage habits not only protects your data but also strengthens your overall security posture. Make safety a routine, not an afterthought.
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Fall yard work Picks
leaf blowers
As an affiliate, we earn on qualifying purchases.