You should keep your cloud authentication diagram current because it visually maps the flow of user identities, credential validation, and access controls. Regular updates help you identify vulnerabilities, incorporate new security measures like multi-factor authentication, and guarantee compliance. By doing this, you improve security posture and response times. Staying up-to-date means your team can quickly adapt to evolving threats and system changes. If you continue, you’ll discover how to effectively maintain and utilize your diagram for maximum security.
Listen free for 30 days with Audible
Thousands of audiobooks and originals — cancel anytime.
As an affiliate, we earn on qualifying purchases.
Key Takeaways
- Regularly review and update diagrams to reflect evolving authentication methods and system changes.
- Clearly depict all authentication components, including identity providers, MFA, and security layers.
- Highlight points of credential verification and secure data transmission for compliance and security.
- Incorporate new security protocols and access policies to maintain comprehensive security coverage.
- Use updated diagrams to identify vulnerabilities and support incident response efforts effectively.
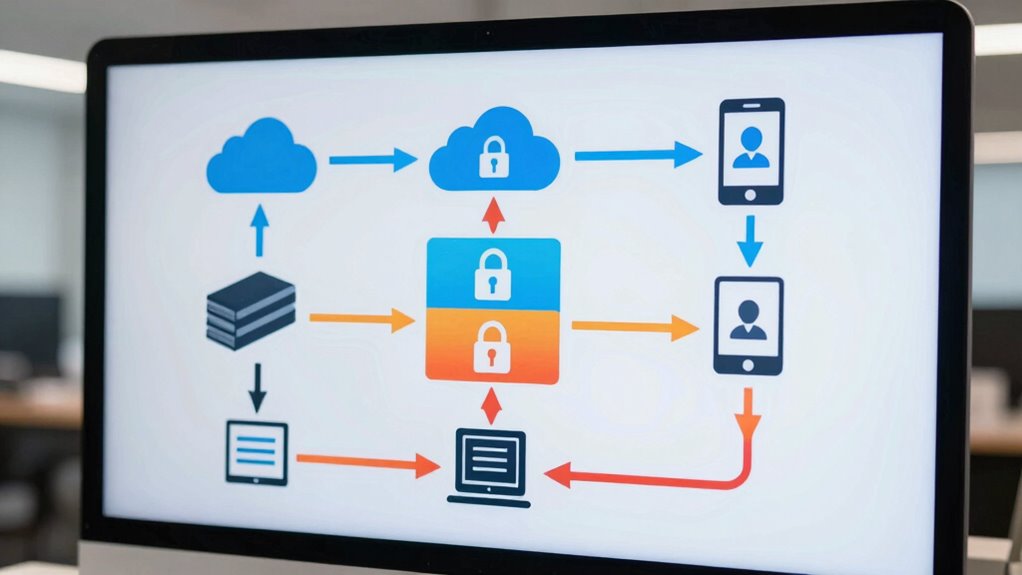
Are you looking to understand how cloud authentication works? If so, it’s essential to recognize that this process centers around verifying user identities and managing access control efficiently. When you log into a cloud service, the system performs identity verification to confirm you are who you claim to be. This step is crucial because it establishes a trusted connection between you and the cloud environment, preventing unauthorized access. Once your identity is verified, access control mechanisms determine what resources you can reach and what actions you can perform. These controls are vital in safeguarding sensitive data and ensuring users only access what they’re permitted to.
A well-designed cloud authentication diagram visually maps the flow of authentication requests, responses, and decision points. It clearly shows how user credentials are submitted and validated, often involving multiple layers like identity providers, authentication servers, and directory services. By keeping this diagram up to date, your security team can quickly identify potential vulnerabilities or bottlenecks in the authentication flow. For example, if a new authentication method is introduced—such as biometric verification or multi-factor authentication (MFA)—the diagram should be revised to include these elements. This guarantees everyone understands how these new layers fit into the overall access control scheme, maintaining clarity and consistency.
Furthermore, an accurate cloud authentication diagram helps in establishing a robust security posture. It highlights the points where identity verification occurs and how credentials are transmitted and stored securely, often through encryption. This clarity allows your team to enforce best practices, such as limiting credential exposure and implementing zero-trust principles. Additionally, understanding secure credential management is essential for maintaining the integrity of authentication processes. Regularly reviewing and updating this diagram can also support compliance efforts, as many regulations require detailed documentation of authentication and access control processes. When updates happen—like integrating a new identity verification provider or adjusting access policies—your diagram should reflect these changes. This practice guarantees your security team can respond swiftly to evolving threats and maintain an all-encompassing understanding of your cloud security architecture.
multi-factor authentication hardware token
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Frequently Asked Questions
How Often Should Cloud Authentication Diagrams Be Reviewed and Updated?
You should review and update your cloud authentication diagrams at least quarterly, or whenever there’s a significant change in access control or identity mapping. Regular updates guarantee your diagrams accurately reflect current security policies, user roles, and access points. This way, you can quickly identify vulnerabilities, maintain proper access control, and adapt to evolving cloud environments, keeping your organization’s security posture strong and up-to-date.
What Are Common Pitfalls in Creating Cloud Authentication Diagrams?
You might overlook the importance of clear access control and identity management, leading to flawed cloud authentication diagrams. Common pitfalls include assuming trust in default settings, neglecting to update diagrams after infrastructure changes, and oversimplifying complex access hierarchies. These mistakes can create gaps in security, making it easier for unauthorized users to gain access. Always guarantee your diagrams accurately reflect current access controls and identity management practices to avoid these vulnerabilities.
How Do Different Cloud Providers’ Authentication Methods Vary?
You’ll notice that different cloud providers vary in their authentication methods, especially regarding identity federation and multi-factor authentication. Some, like AWS, support single sign-on with external identity providers, enabling seamless federation. Others, like Azure, emphasize integrated multi-factor authentication for enhanced security. These differences influence how you implement secure access controls, making it vital to understand each provider’s approach to guarantee your cloud environment stays protected.
What Security Risks Are Associated With Outdated Cloud Authentication Diagrams?
Like using a dial-up modem in a fiber-optic world, outdated cloud authentication diagrams pose serious security risks. You risk weak access control and flawed identity management, making it easier for intruders to exploit vulnerabilities. Without current diagrams, you might overlook critical changes, leaving gaps in your security. This can lead to unauthorized access, data breaches, and compromised systems, all of which threaten your organization’s integrity and trust.
Which Tools Are Best for Designing and Maintaining Cloud Authentication Diagrams?
You should use tools like Microsoft Visio, Lucidchart, or Draw.io for designing and maintaining cloud authentication diagrams. These tools excel at access management and diagram visualization, allowing you to create clear, accurate representations of your cloud security architecture. They also support collaboration and version control, helping you keep diagrams up-to-date as your environment evolves. Regularly updating these diagrams guarantees your security team can quickly identify and address potential vulnerabilities.
As an affiliate, we earn on qualifying purchases.
Conclusion
Staying updated with the cloud authentication diagram keeps your security sharp—like a shield protecting your digital world. But neglecting it leaves gaps, vulnerabilities you might never see until it’s too late. In a landscape where threats evolve faster than you can blink, your vigilance becomes your strongest defense. Don’t let complacency be your downfall. Keep that diagram current, and remember: in security, awareness isn’t just power—it’s your lifeline.
As an affiliate, we earn on qualifying purchases.
secure credential management solutions
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
NFL season / tailgating Picks
team gear
As an affiliate, we earn on qualifying purchases.