Choosing the right firewall appliance for zero trust segmentation in 2026 means balancing performance, security features, deployment complexity, and cost. If I were selecting for a small business, the SonicWall TZ280 offers a solid throughput at an attractive price, but it requires additional security subscriptions. For mid-sized organizations, the Sophos XGS 118 provides high performance and SD-WAN capabilities but involves extra licensing. The WatchGuard Firebox T185 stands out for demanding branch sites with its comprehensive security suite and fiber uplinks. Each option caters to different needs, with notable tradeoffs in management complexity, cost, and scalability.

Get business pricing on networking and server gear
- Business-only prices and quantity discounts
- Tax-exempt purchasing
- Multiple users, one account, clear invoices
Key Takeaways
- Performance varies significantly; choose based on network size and throughput needs.
- Security features are often sold as add-ons; consider total cost of ownership.
- Ease of deployment and management can differ, impacting operational overhead.
- Larger organizations may require more scalable, feature-rich solutions.
- Price point often correlates with security depth and hardware capabilities.
| SonicWall TZ280 2.5 Gbps Next-Gen Firewall Appliance |  | Best for Small Business and Branch Offices | Performance: Up to 2.5 Gbps firewall inspection | Threat Prevention Throughput: 1 Gbps | VPN Throughput: 1.2 Gbps | VIEW ON AMAZON | See Our Full Breakdown |
| FortiGate 40F Firewall Appliance – 5 Gigabit Ethernet Ports, Small Business Security |  | Best for Compact, Quiet Office Environments | Ports: 5 Gigabit Ethernet RJ45 ports | WAN ports: 1 | Internal ports: 4 | VIEW ON AMAZON | See Our Full Breakdown |
| Sophos XGS 118 (Gen2) Network Security Appliance |  | Best for Mid-Sized Organizations Needing Advanced Security | Ports: 9 x 2.5 GE copper, 1 SFP | Performance: Up to 15.5 Gbps firewall throughput | Features: Next-generation firewall, SD-WAN, VPN, cloud-based management | VIEW ON AMAZON | See Our Full Breakdown |
| Meraki MX75-HW Security Appliance Bundle | 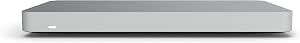 | Best for Small Deployments with Cloud Management | Throughput: 1 Gbps | VPN Throughput: 500 Mbps | WAN Ports: 3 (1x SFP, 2x GbE) | VIEW ON AMAZON | See Our Full Breakdown |
| WatchGuard Firebox T185 with 5-Year Total Security Suite |  | Best for Demanding Branch and Retail Sites | Model: Firebox T185 | Security Suite: 5-Year Total Security | Ports: SFP+, 2.5Gb, 1Gb ports | VIEW ON AMAZON | See Our Full Breakdown |
| firewall appliance for zero trust segmentation | Ports |
|---|---|
| SonicWall TZ280 2.5 Gbps Next- | 8x1GbE, 2x1G SFP |
| FortiGate 40F Firewall Applian | 5 Gigabit Ethernet RJ45 ports |
| Sophos XGS 118 | 9 x 2.5 GE copper, 1 SFP |
| Meraki MX75-HW Security Applia | — |
| WatchGuard Firebox T185 with 5 | SFP+, 2.5Gb, 1Gb ports |
More Details on Our Top Picks
SonicWall TZ280 2.5 Gbps Next-Gen Firewall Appliance
The SonicWall TZ280 stands out for delivering up to 2.5 Gbps inspection throughput, making it suitable for small business environments that need reliable, high-speed security. Its multiple connectivity options, including SFP ports, enhance network flexibility. While it offers advanced security features like sandboxing, TLS decryption, and intrusion prevention, these require separate purchases, which can increase the total cost. Compared to more integrated solutions, this appliance emphasizes raw performance and deployment simplicity but falls short on out-of-the-box security subscriptions. This pick makes the most sense for organizations that prioritize performance and are comfortable managing security separately.
Pros:- High firewall throughput suitable for small business needs
- Multiple connectivity options including SFP ports
- Supports advanced security features like sandboxing and TLS decryption
- Easy deployment and management
Cons:- Hardware only; security services require additional purchase
- Limited to small business and branch environments
- No included security subscription or firmware updates
Best for: Small businesses or branch offices needing straightforward, high-throughput security
Not ideal for: Organizations seeking an all-in-one, subscription-inclusive platform or larger enterprise environments
- Performance:Up to 2.5 Gbps firewall inspection
- Threat Prevention Throughput:1 Gbps
- VPN Throughput:1.2 Gbps
- Ports:8x1GbE, 2x1G SFP
- Form Factor:Desktop
- Security Features:Intrusion prevention, anti-malware, application control, TLS/SSL decryption, sandboxing, DNS filtering
Our verdict“A strong choice for small businesses prioritizing high throughput and flexible connectivity, provided they are prepared for additional security licensing.”
FortiGate 40F Firewall Appliance – 5 Gigabit Ethernet Ports, Small Business Security
The FortiGate 40F offers a compact, fanless design ideal for small to mid-sized businesses that need high-performance security without noise. Its 1 Gbps IPS throughput, combined with five Gigabit Ethernet ports, simplifies management and enhances network resilience. However, it does not include subscription services, so additional costs may be necessary for full security features. Compared with the SonicWall TZ280, it provides a more integrated security experience with less configuration fuss, but it’s less scalable for larger networks. This device makes sense for smaller organizations seeking a quiet, easy-to-manage security appliance with solid performance.
Pros:- Compact and fanless design for quiet operation
- High-performance security with industry-leading throughput
- Easy to deploy and manage with user-friendly console
Cons:- No subscription services included
- Limited to small/mid-sized environments
Best for: Small to mid-sized businesses looking for a silent, easy-to-deploy firewall
Not ideal for: Organizations requiring extensive security subscriptions or larger, more complex deployments
- Ports:5 Gigabit Ethernet RJ45 ports
- WAN ports:1
- Internal ports:4
- Throughput:1 Gbps IPS, 600 Mbps threat protection
Our verdict“An excellent choice for small to mid-sized organizations wanting a quiet, straightforward security device with reliable throughput.”
Sophos XGS 118 (Gen2) Network Security Appliance
The Sophos XGS 118 (Gen2) is designed for mid-sized organizations demanding high throughput and versatile connectivity. Its impressive 15.5 Gbps firewall throughput supports complex, high-demand environments, with nine 2.5 GE ports plus an SFP port for flexible networking. It integrates SD-WAN, VPN, and cloud management, making it a comprehensive solution. However, its advanced security features require additional licensing, which can increase costs. Compared to smaller appliances, the XGS 118 offers scalability and performance but demands a larger budget and more management effort. It’s well-suited for organizations with sizable, security-focused networks willing to invest in licensing and configuration complexity.
Pros:- High firewall performance suitable for demanding environments
- Multiple port options for flexible connectivity
- Built-in SD-WAN for resilient connectivity
Cons:- Requires a subscription for advanced security features
- Additional licenses needed for full functionality
Best for: Mid-sized organizations with high throughput needs and multi-site connectivity
Not ideal for: Small businesses or organizations seeking a simple, all-in-one plug-and-play solution
- Ports:9 x 2.5 GE copper, 1 SFP
- Performance:Up to 15.5 Gbps firewall throughput
- Features:Next-generation firewall, SD-WAN, VPN, cloud-based management
Our verdict“A powerful, scalable option for mid-sized businesses prioritizing high throughput and flexible connectivity, with a tradeoff in licensing complexity.”
Meraki MX75-HW Security Appliance Bundle
The Meraki MX75-HW offers a cloud-managed approach tailored for small branch deployments. Its 1 Gbps throughput, three WAN ports (including SFP), and integrated SD-WAN and VPN make it simple to set up and manage remotely. The zero-touch provisioning and cloud interface streamline deployment, but the absence of included licenses means ongoing costs for advanced features. Compared to traditional appliances, it greatly reduces management overhead but might lack the raw performance or feature depth needed for larger or more demanding networks. This device suits small organizations wanting cloud-based control with straightforward security and connectivity.
Pros:- High-performance firewall with 1 Gbps throughput
- Integrated SD-WAN and VPN for multi-site connectivity
- Cloud-managed with zero-touch provisioning
- Advanced threat protection including intrusion prevention
Cons:- No license included; additional costs for features
- Designed for small deployments, not scalable for large networks
Best for: Small branches or remote sites seeking cloud-managed simplicity
Not ideal for: Larger networks or organizations needing extensive on-premises control
- Throughput:1 Gbps
- VPN Throughput:500 Mbps
- WAN Ports:3 (1x SFP, 2x GbE)
- User Capacity:Up to 200 users
Our verdict“An ideal lightweight, cloud-centric security appliance for small branches with minimal on-site management needs.”
WatchGuard Firebox T185 with 5-Year Total Security Suite
The WatchGuard Firebox T185 is crafted for high-demand branch or retail environments needing comprehensive security. It offers multiple SFP+, 2.5Gb, and 1Gb ports, supporting up to 1.83 Gbps of UTM throughput. Its standout feature is the long-term 5-year Total Security Suite that combines AI-driven malware detection, DNS filtering, and cloud sandboxing, delivering extensive, ongoing protection. The appliance’s complexity and higher price tag reflect its enterprise-level capabilities. Compared to other options, it emphasizes security depth and fiber uplink options, making it suitable for organizations with serious security requirements and available budgets. It may be overkill for small, less demanding setups.
Pros:- High-speed fiber uplinks with multiple port options
- Comprehensive security suite with AI-driven malware detection
- Long-term license coverage (5 years)
- Designed for high-demand environments
Cons:- Primarily enterprise-focused; may be complex for small setups
- Higher price point reflecting extensive features
Best for: Branches or retail locations with high security requirements and fiber connectivity needs
Not ideal for: Small or simple networks with limited budgets or less complex security needs
- Model:Firebox T185
- Security Suite:5-Year Total Security
- Ports:SFP+, 2.5Gb, 1Gb ports
- UTM Throughput:1.83 Gbps
Our verdict“A robust, security-centric appliance best suited for large, security-critical sites with demanding throughput and connectivity needs.”

How We Picked
Our selection process focused on appliances that are explicitly designed or capable of supporting zero trust segmentation. We prioritized products that offer high throughput, robust security features, and flexible connectivity options suitable for different organizational sizes. We compared hardware performance, security capabilities, ease of management, and scalability, while also considering the need for additional licenses or subscriptions. Cost effectiveness and deployment simplicity were also key factors, ensuring each product provides a clear value proposition for its target environment.
Factors to Consider When Choosing Firewall Appliance For Zero Trust Segmentation
Selecting a firewall appliance for zero trust segmentation requires understanding your network’s size, security needs, and management capacity. The right device should balance throughput, security features, and ease of use, while considering future scalability. It’s vital to assess whether you prefer a standalone hardware solution, a cloud-managed device, or a hybrid approach that can grow with your organization.
Performance and Throughput
Evaluate your network’s bandwidth demands. Small offices might suffice with appliances offering 1 Gbps throughput, while larger or high-demand sites require models supporting 10 Gbps or more. Remember, higher throughput often means higher cost and complexity, but is essential for maintaining seamless zero trust segmentation without bottlenecks.
Security Features and Licensing
Not all security features come standard; many appliances require additional licenses for advanced threat protection, sandboxing, or SD-WAN. Consider the total cost of ownership, and whether the device includes necessary subscriptions or if these will be an ongoing expense. Prioritize appliances that align security capabilities with your organization’s risk profile.
Connectivity and Scalability
Check the number and type of ports—Ethernet, fiber, SFP—matching your current infrastructure and future growth plans. Some appliances excel in small settings, while others are designed to scale for larger, distributed networks. Think about management complexity—cloud-based options often simplify multi-site deployments but may require ongoing subscriptions.
Ease of Deployment and Management
Ease of use varies widely; products like Meraki emphasize zero-touch deployment and cloud management, ideal for teams with limited on-site expertise. Conversely, more traditional appliances might offer deeper customization but demand more in-house management. Determine your team’s technical capacity and choose accordingly.
Frequently Asked Questions
What is zero trust segmentation?
Zero trust segmentation involves dividing your network into smaller, isolated segments, each with strict access controls. This approach minimizes the risk of lateral movement by attackers and enforces continuous verification of users and devices, making your network significantly more secure.
How does throughput impact zero trust deployment?
Throughput determines how much network traffic a firewall can inspect and process without causing bottlenecks. For zero trust segmentation, high throughput ensures that security measures like deep packet inspection do not slow down critical applications, especially in environments with substantial data flow or high-performance needs.
Are security subscriptions necessary for zero trust?
Many appliances require additional security licenses for features like sandboxing, advanced threat detection, or SD-WAN. While these add to the initial cost, they often provide essential layers of security crucial for effective zero trust segmentation, which relies on continuous, adaptive threat prevention.
Can small appliances support zero trust segmentation?
Yes, small appliances can support zero trust segmentation if the organization’s network is limited in size and complexity. However, they may lack advanced features or scalability needed for larger or more dynamic environments, requiring careful assessment of future growth plans.
Is cloud management better for zero trust networks?
Cloud management simplifies deployment, monitoring, and policy enforcement across multiple sites, making it appealing for zero trust architectures that span distributed environments. However, it introduces ongoing subscription costs and potential dependency on external providers, which organizations should evaluate against their security policies.
Conclusion
For small businesses or branch offices, appliances like the SonicWall TZ280 or Meraki MX75-HW offer straightforward, high-performance security with manageable complexity. Mid-sized organizations should consider the Sophos XGS 118 for its scalability and advanced features, while larger enterprises with demanding security needs might find the WatchGuard Firebox T185 or the Sophos XGS 118 better suited. Each buyer should weigh current network demands, future growth, and budget constraints to select the appliance that best aligns with their zero trust segmentation strategy.
Halloween Picks
halloween
As an affiliate, we earn on qualifying purchases.